
PoSH-R2 is a set of Windows Management Instrumentation (WMI) scripts that investigators and forensic analysts can use to retrieve information from a compromised (or potentially compromised) Windows system. The scripts use WMI to pull this information from the operating system. Therefore, this script will need to be executed with a user that has the necessary privileges and authentication is done via a Network logon. Retreived data is written to CSVs and SQLite databases on the system running the script.
In a single execution, PoSH-R2 will retrieve the following data from an individual machine or a group of systems:
- Autorun entries
- Disk info
- Environment variables
- Event logs (50 lastest)
- Installed Software
- Logon sessions
- List of drivers
- List of mapped network drives
- List of running processes
- Logged in user
- Local groups
- Local user accounts
- Network configuration
- Network connections
- Patches
- Scheduled tasks with AT command
- Shares
- Services
- System Information
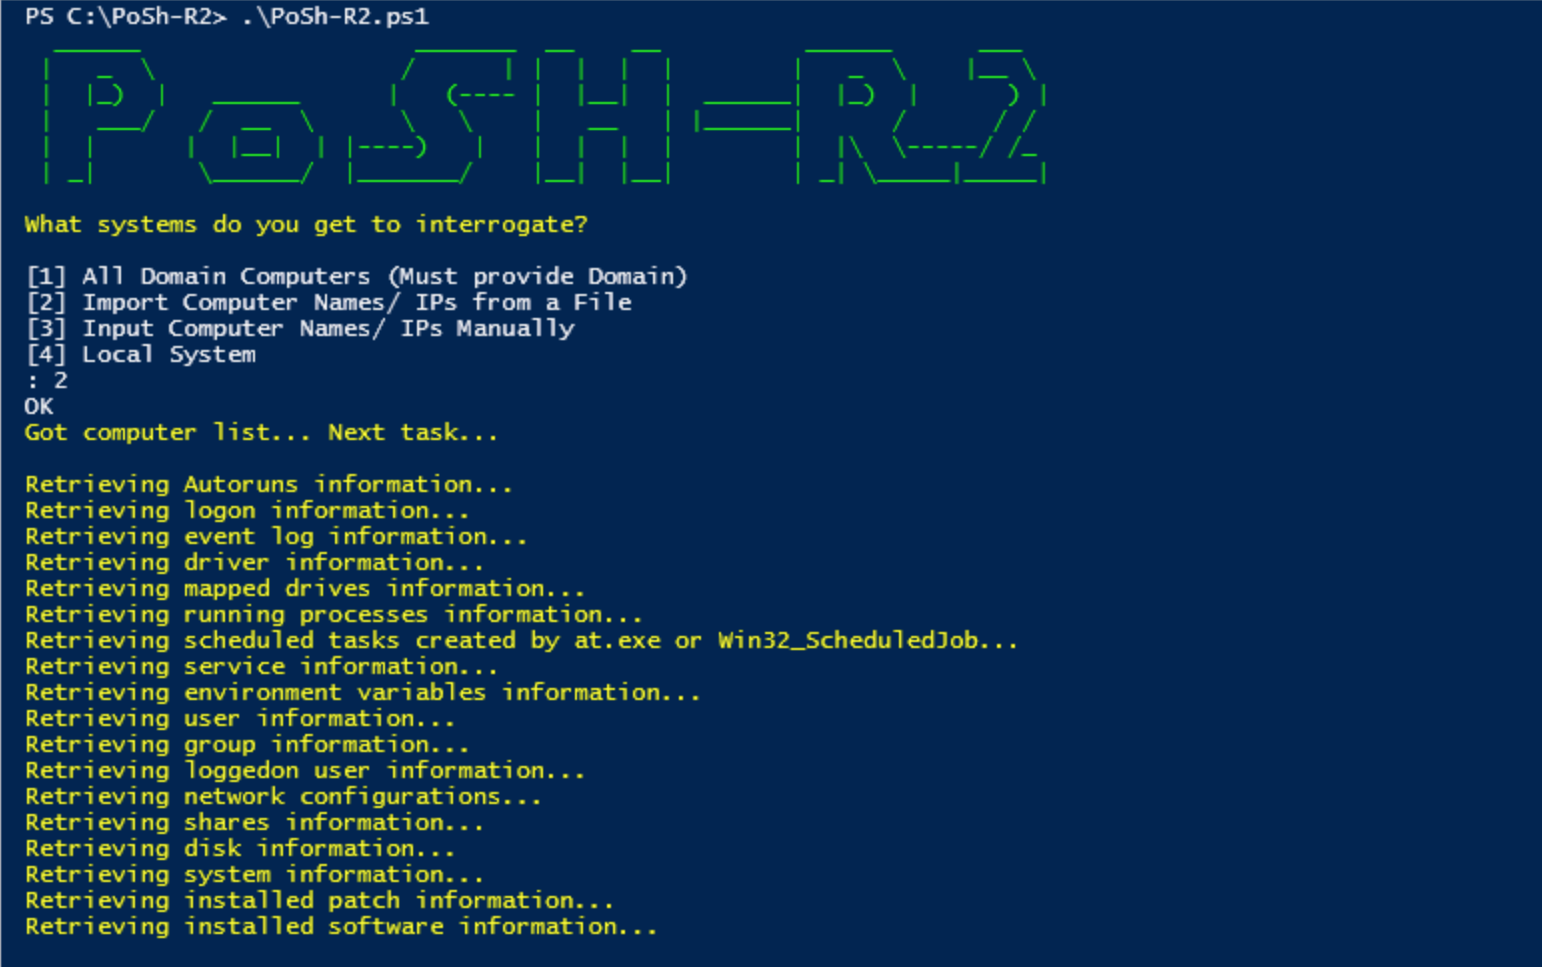
- Call upon the script from a PowerShell window with applicable rights for WMI and follow the prompts.
- Data will be saved to a new directory called "PoSH_R2--Results" within the same directory from which this script was executed from.
- This script will work with PowerShell version 2 and above
Running the script
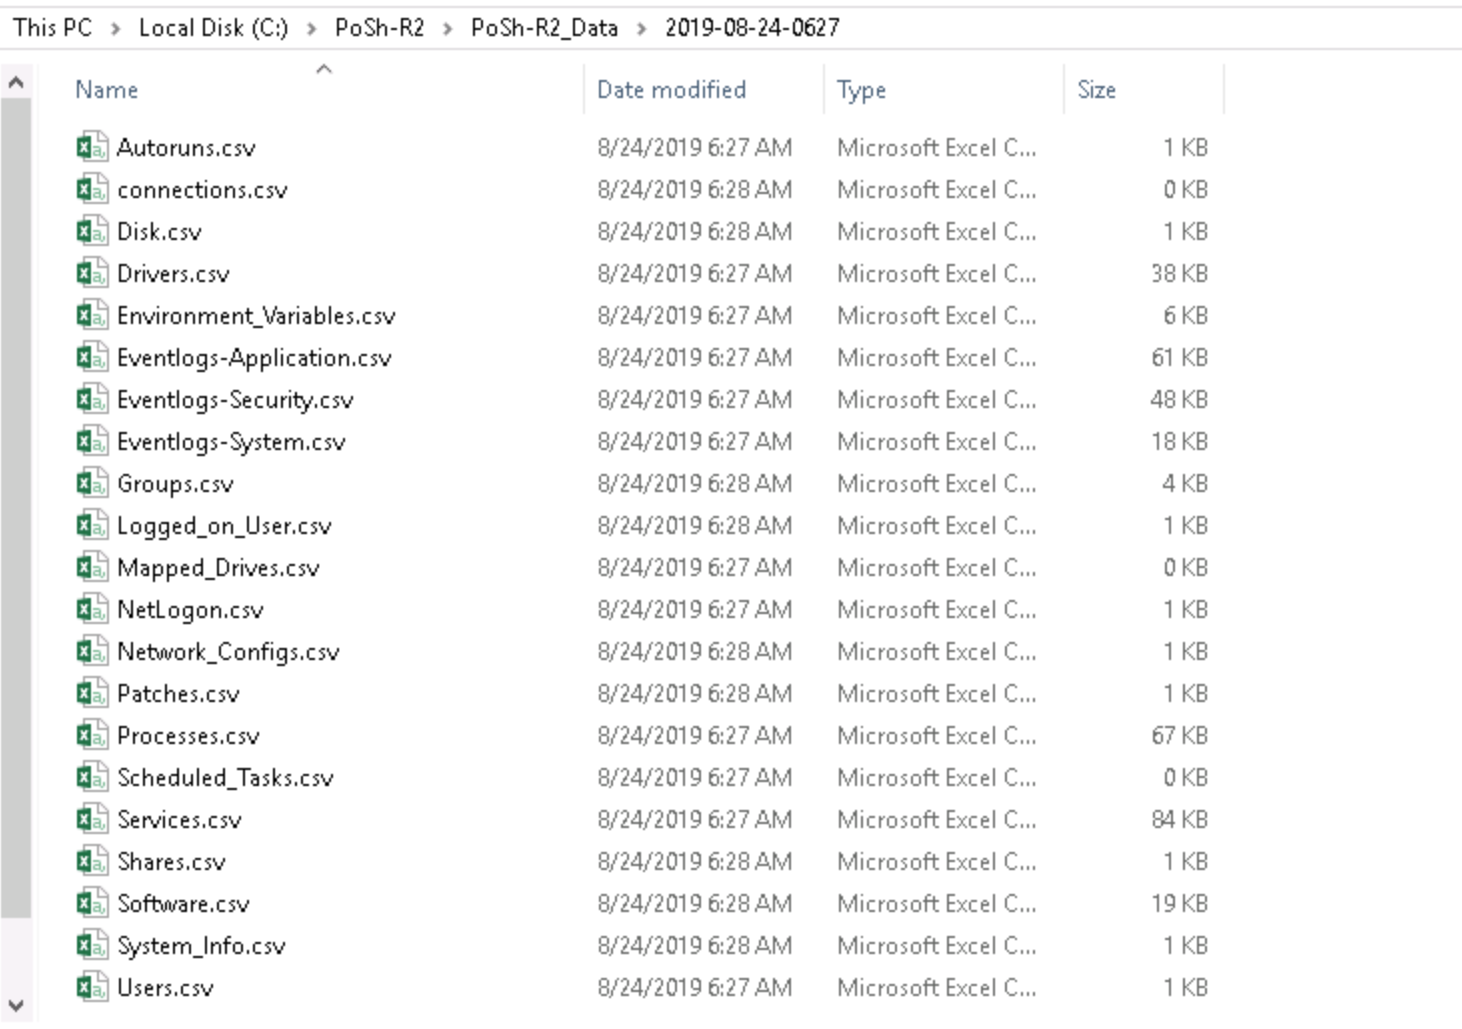
A listing of the results written to csv files
A listing of the databases

Reading the data back into PowerShell using out-gridview (import-csv .<some_file.csv> | out-gridview)

Filtering only on splunk.exe. From the screenshot, we see it is running on six systems
